Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
The first SBOM-powered platform for securing your software supply chain.
Anchore Enterprise is the first SBOM-powered software supply chain management platform for continuous security and compliance.
Manage internal and external SBOMs in a single location to track software supply chain issues.
Ensure the security of software products you release or host as SaaS and provide SBOMs and assurance for your customers.
Embed security and compliance checks into each step of your development lifecycle for more secure cloud-native and legacy applications.
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Pricing Overview
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
The first SBOM-powered platform for securing your software supply chain.
Anchore Enterprise is the first SBOM-powered software supply chain management platform for continuous security and compliance.
Manage internal and external SBOMs in a single location to track software supply chain issues.
Ensure the security of software products you release or host as SaaS and provide SBOMs and assurance for your customers.
Embed security and compliance checks into each step of your development lifecycle for more secure cloud-native and legacy applications.
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Pricing Overview
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Anchore Blog.
Blog
How Syft Scans Software to Generate SBOMs
Syft is an open source CLI tool and Go library that generates a Software Bill of ...
Read the Blog
Blog
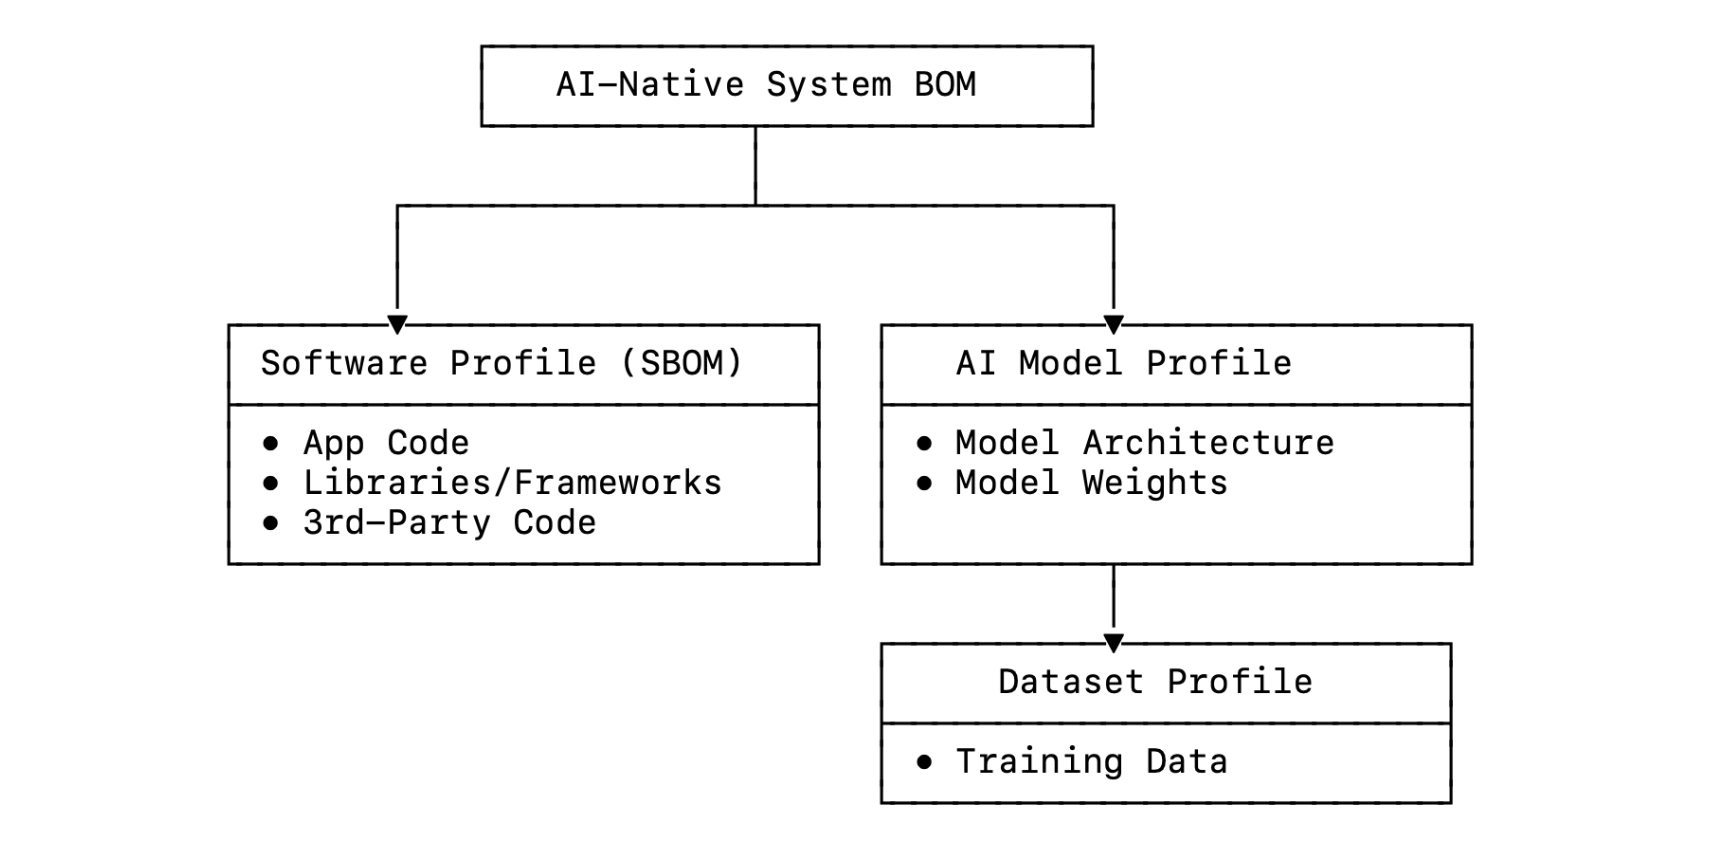
Beyond Software Dependencies: The Data Supply Chain Security Challenge of AI-Native Applications
Read the Blog
Blog
EU CRA SBOM Requirements: Overview & Compliance Tips
Read the Blog
Blog
NIST 800-37, the Risk Management Framework: A Guide in Plain English
Read the Blog
Filter
Clear
Apply
Filter
By Topic
ATO & cATO
Attack Prevention
Best Practices
CI/CD
Cloud Environments
Comparisons
Container Registries
Container Security
DevOps
DevSecOps
Docker
Guides & How To
Industry News
Integrations
Kubernetes
Log4J
Open Source
Policy & Compliance Standards
Products
Public Sector
Remediation
SBOM (Software Bill of Materials)
STIG
Scanning
Software Supply Chain
Vulnerabilities
View More
Culture
Be Yourself With Us
Humans of Anchore
Mission: Impact
Blog
Navigating the NVD Quagmire
Read the Blog
Blog
Spring Webinar Update: Expand Your Knowledge with Our Expert-Led Sessions
Read the Blog
Blog
National Vulnerability Database: Opaque changes and unanswered questions
Read the Blog
Blog
Syft Reaches v1.0!
Read the Blog
Blog
Anchore Enterprise 5.1: Token-Based Authentication
Read the Blog
Blog
Introducing Grant: A new OSS project from Anchore for inspecting and checking license compliance from SBOMs
Read the Blog
Blog
Introducing VIPERR: The First Software Supply Chain Security Framework for All
Read the Blog
Blog
NIST CSF 2.0: Key Takeaways and Implementation Strategies
Read the Blog
Blog
Anchore Enterprise 5.0: New, Free Self-Service Trial
Read the Blog
Blog
Unpacking the Power of Policy at Scale in Anchore
Read the Blog
Blog
Introducing Anchore Enterprise 5.0
Read the Blog
Blog
SBOMs & Vulnerability Scanners: Better Together
Read the Blog
Blog
Guide to SBOMs: What They are and Their Role in Cybersecurity
Read the Blog
Blog
Say Goodbye to False Positives
Read the Blog
Blog
Detecting Exploits within your Software Supply Chain
Read the Blog
Blog
Introducing Grype Explain
Read the Blog
Blog
How to Scan Your Containers for Vulnerabilities with Free Open Source Tools
Read the Blog
Blog
NIST’s Comprehensive Approach to Software Supply Chain Security
Read the Blog
Blog
Scaling Software Security with NVIDIA
Read the Blog
Blog
Automated Policy Enforcement for CMMC with Anchore Enterprise
Read the Blog
Blog
Breaking Down NIST SSDF: Spotlight on P0.1 – Prepare the Organization
Read the Blog
Blog
NIST SP 800-53, the Control Catalog: A Guide in Plain English
Read the Blog
Blog
NIST 800-37, the Risk Management Framework: A Guide in Plain English
Read the Blog
Blog
Four Signs You’re Ready to Upgrade from DIY Supply Chain Security to Anchore Enterprise
Read the Blog
Blog
Software Supply Chain Hierarchy of Needs: SBOMs as the Foundation
Read the Blog
Blog
Customizing Grype Vulnerability Reports With Templates
Read the Blog
Blog
Anchore OSS Now Supports Microsoft’s Azure Linux
Read the Blog
Blog
From Code to Cloud: Anchore Delivers SBOM-Powered SCA
Read the Blog
Blog
Amazon ECS and Anchore Enterprise: Big Updates
Read the Blog
Blog
Breaking Down NIST SSDF: Spotlight on PW.6 – Build Systems
Read the Blog
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
No results found