Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
The first SBOM-powered platform for securing your software supply chain.
Anchore Enterprise is the first SBOM-powered software supply chain management platform for continuous security and compliance.
Manage internal and external SBOMs in a single location to track software supply chain issues.
Ensure the security of software products you release or host as SaaS and provide SBOMs and assurance for your customers.
Embed security and compliance checks into each step of your development lifecycle for more secure cloud-native and legacy applications.
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Pricing Overview
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
The first SBOM-powered platform for securing your software supply chain.
Anchore Enterprise is the first SBOM-powered software supply chain management platform for continuous security and compliance.
Manage internal and external SBOMs in a single location to track software supply chain issues.
Ensure the security of software products you release or host as SaaS and provide SBOMs and assurance for your customers.
Embed security and compliance checks into each step of your development lifecycle for more secure cloud-native and legacy applications.
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Platform
Platform Overview
SBOM Management
Secure & Protect
Automated Compliance
Open Source
Public Sector
Anchore Federal
NIST Compliance
DoD Software Factory
Use Cases
SBOM Management
Container Vulnerability Scanning
EU CRA Compliance
FedRAMP Vulnerability Scanning
Federal Compliance
Software Supply Chain Security
Resources
Resource Hub
All Resources
Case Studies
White Papers
Webinars
Blog
Events
Developer Hub
Open Source
Enterprise Documentation
Integrations
Knowledge Center
Compliance
SBOM
Software Supply Chain Security
Pricing
Pricing Overview
Company
About Us
Support Portal
Partners
Careers & Culture
Press & News
Contact Us
Free Trial
Anchore Blog.
Blog
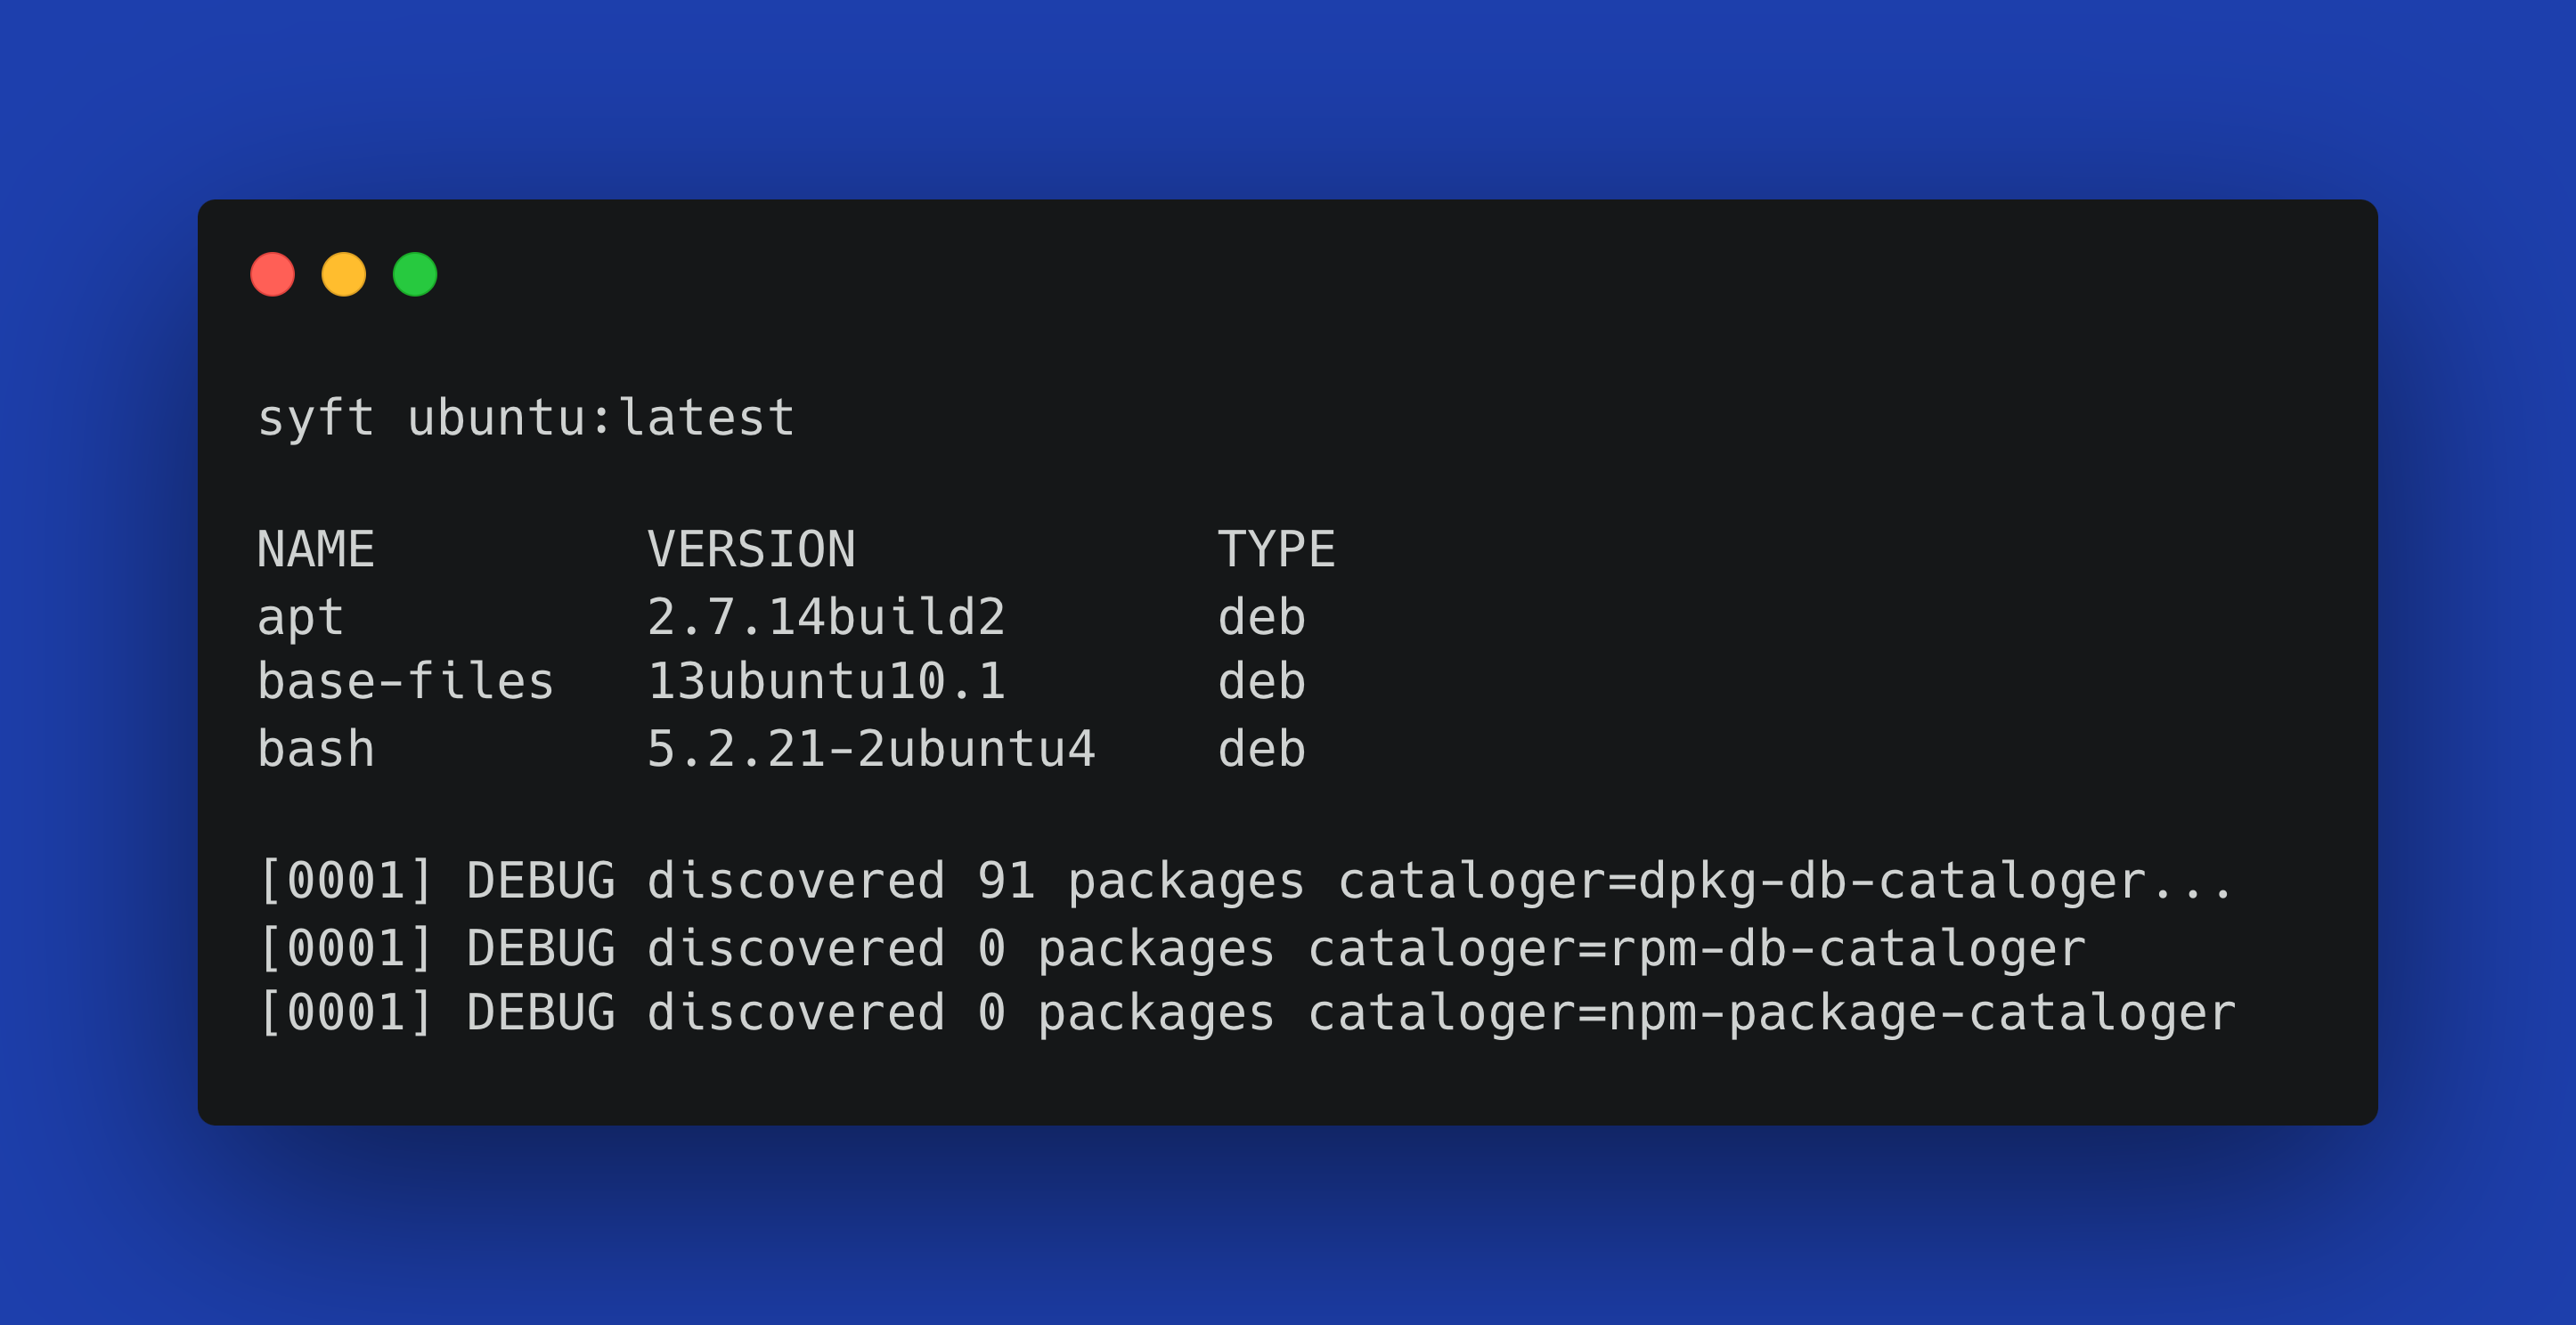
How Syft Scans Software to Generate SBOMs
Syft is an open source CLI tool and Go library that generates a Software Bill of ...
Read the Blog
Blog
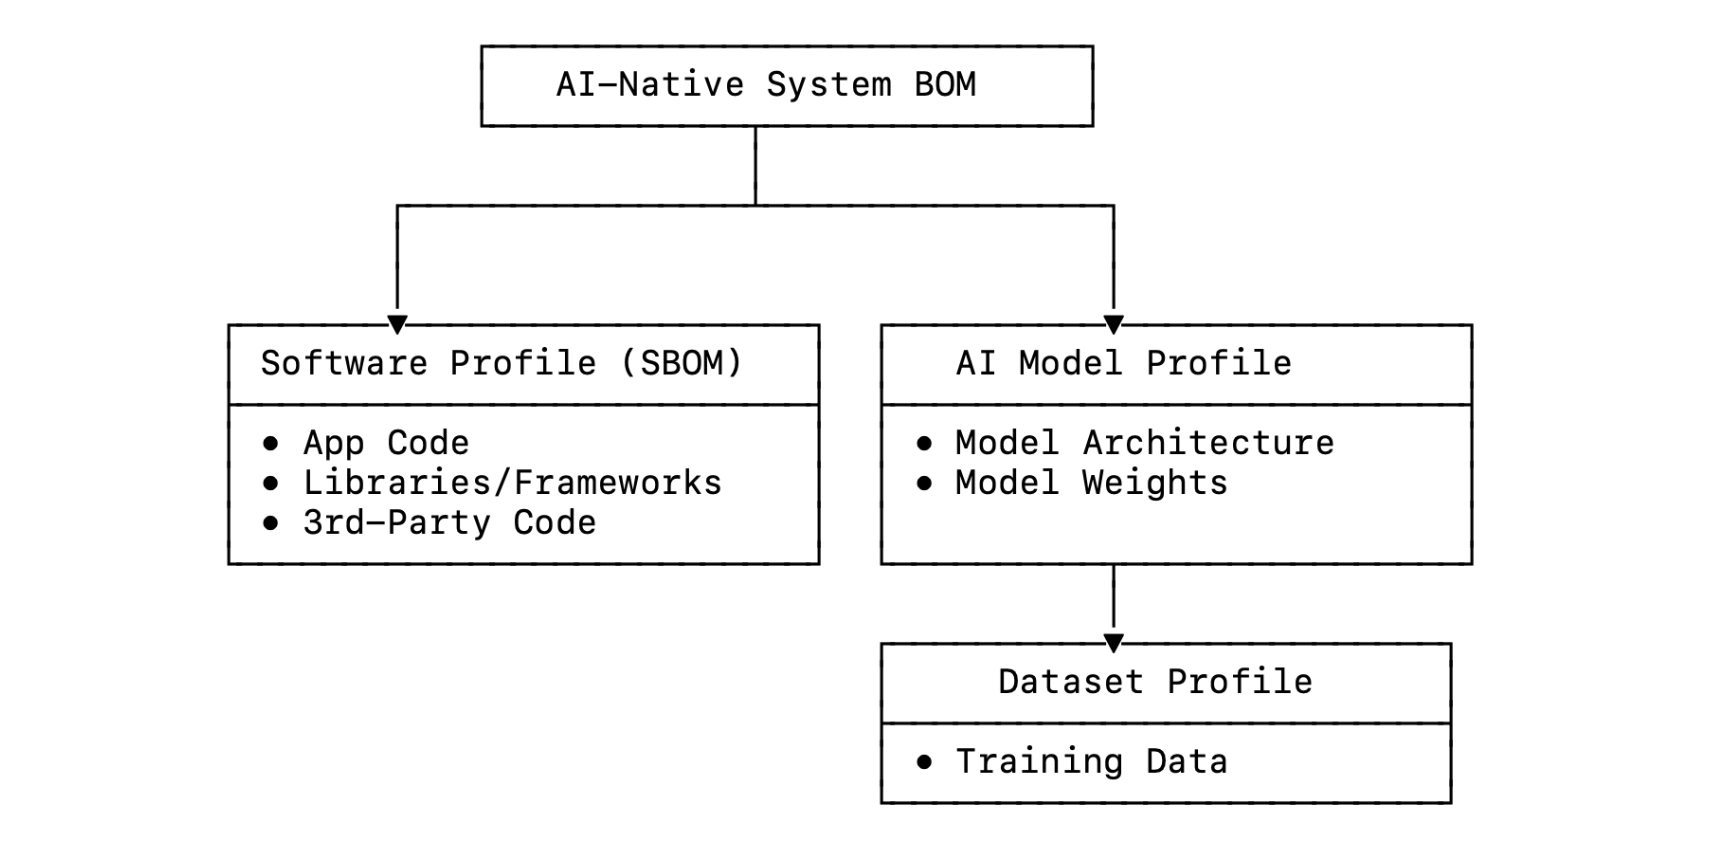
Beyond Software Dependencies: The Data Supply Chain Security Challenge of AI-Native Applications
Read the Blog
Blog
EU CRA SBOM Requirements: Overview & Compliance Tips
Read the Blog
Blog
NIST 800-37, the Risk Management Framework: A Guide in Plain English
Read the Blog
Filter
Clear
Apply
Filter
By Topic
ATO & cATO
Attack Prevention
Best Practices
CI/CD
Cloud Environments
Comparisons
Container Registries
Container Security
DevOps
DevSecOps
Docker
Guides & How To
Industry News
Integrations
Kubernetes
Log4J
Open Source
Policy & Compliance Standards
Products
Public Sector
Remediation
SBOM (Software Bill of Materials)
STIG
Scanning
Software Supply Chain
Vulnerabilities
View More
Culture
Be Yourself With Us
Humans of Anchore
Mission: Impact
Blog
Node2Shell: Your SBOMs Already Know Which Node.js Builds You’re Running
Read the Blog
Blog
How ServiceNow Covers 90 Container Release Programs With SBOM-Driven Security
Read the Blog
Blog
SBOM Drift Detection: Catch Changes from Build to Production
Read the Blog
Blog
Faster Answers, Fewer False Positives with Anchore Enterprise v6.3
Read the Blog
Blog
PHP2Shell: Your SBOMs Already Know Which PHP Builds You’re Running
Read the Blog
Blog
Anchore is now an OpenChain Partner
Read the Blog
Blog
8 Days to Fix vs. 24 Hours to Report: The EU CRA Compliance Gap
Read the Blog
Blog
Intro to AI-BOMs (AI Bill of Materials)
Read the Blog
Blog
DoW Instruction 8430.01 makes software evidence a condition to operate
Read the Blog
Datasheet
Anchore DoWI 8430.01 SBOM Requirements
Download the Datasheet
Blog
Bridging the Cybersecurity Divide: How SBOM Management Empowers Developing Nations
Read the Blog
Blog
Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise
Read the Blog
Blog
What EU CRA’s 24-hour deadline means for your SBOM
Read the Blog
Blog
FedRAMP & CMMC in 2026: what actually changed for your Authority to Operate (ATO)
Read the Blog
Blog
Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2
Read the Blog
Blog
What Your Vulnerability Scan Misses The Moment a Zero-Day Drops
Read the Blog
Blog
Anchore + AI Just Got Easier: The Anchore Enterprise MCP Server
Read the Blog
Blog
Your Kubernetes cluster is running images your registry scan never checked
Read the Blog
Blog
Silence Is Now a Statement: Why CISA’s 2026 SBOM Minimum Elements Are a Real Improvement
Read the Blog
Blog
One SBOM, five auditors! How you can map software inventory to ISO 27001, SOC 2, PCI DSS 4.0.1, HIPAA, and NIST SSDF
Read the Blog
Blog
Operationalizing SBOMs to Boost Incident Response Velocity with Anchore Enterprise v6.1
Read the Blog
Blog
What your SBOM inventory misses if it only covers containers
Read the Blog
Blog
CompOps in the agentic era: a blueprint for continuous compliance
Read the Blog
Blog
“You Own the Problem”: Red Hat and Bitsea on Getting Ready for the EU CRA
Read the Blog
Blog
The EU CRA Reporting Deadline Is 45 Days Out. Here’s What You Need.
Read the Blog
Blog
EU CRA Compliance Checklist: 5 Steps to Prepare Now
Read the Blog
Blog
From SBOM Visibility to Action: Operationalizing VEX in Container Security Pipelines
Read the Blog
Blog
EU CRA Vulnerability Management: Requirements, Deadlines, and Compliance Tips
Read the Blog
Blog
Automating Administrative Tasks via the Anchore Enterprise API
Read the Blog
Blog
From the Field: How to Automate CMMC compliance for containers & SBOMs with Anchore Enterprise
Read the Blog
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
No results found
Speak with our security experts
Learn how Anchore’s SBOM-powered platform can help secure your software supply chain.
Contact Us