Automate FedRAMP Vulnerability Scanning and Compliance
If you sell cloud services to federal agencies, your vulnerability program changes on December 7, 2026. That’s when FedRAMP’s Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) rules, required under CISA Binding Operational Directive (BOD) 26-04, apply to Rev 5 and 20x offerings alike. Monthly scans and severity-based deadlines give way to persistent detection and evaluation based on internet reachability, likely exploitability and Potential Agency Impact (PAIN), with as few as 2 days to evaluate each finding. Manual triage and POA&M spreadsheets won’t keep that pace.
Anchore Enterprise provides out-of-the-box capabilities to help meet FedRAMP vulnerability scanning requirements:
- Persistent vulnerability detection from stored SBOMs for containers, hosts, VMs and source code
- CISA KEV, EPSS, CISA SSVC data and Anchore Score on every finding to speed exploitability evaluation
- FedRAMP 20x and NIST policy packs, plus STIG checks to validate hardened images
- Registry and Kubernetes monitoring for complete detection coverage
- Application and version grouping, so one CVE across many images is one tracked response
- SBOM, VEX and VDR exports and SSVC decisions

Navigating to FedRAMP 20x Pivot
In this panel discussion we learn how InfusionPoints took their platform through the FedRAMP 20x pilot. They explain how they automated evidence collection, rebuilt vulnerability triage around KEV status and internet reachability, and what changes for your path to authorization.
Automated FedRAMP container vulnerability scanning and detection
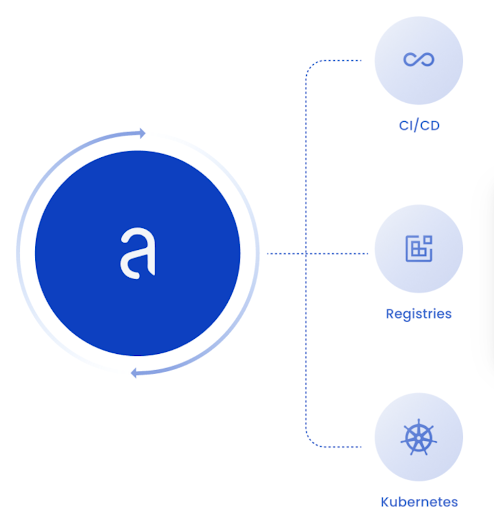
FedRAMP 20x expects persistent detection, not a 30-day scanning window. Automate scans in CI/CD pipelines, registries and Kubernetes, and generate SBOMs for VM and host filesystems, source repositories and third-party software. Anchore re-evaluates every stored SBOM as vulnerability feeds update, so new CVEs surface without a rescan and your team stops rebuilding inventories before every monthly upload. Harden container images by identifying malware, secrets and security risks in addition to vulnerabilities, and perform STIG checks for container images.
Support FedRAMP 20x KSIs and NIST controls
Automate FedRAMP container compliance checks with Anchore’s out-of-the-box policy packs for FedRAMP 20x and NIST security controls. Use the same findings as evidence for FedRAMP 20x Key Security Indicators, including supply chain risk (KSI-SCR), policy and inventory (KSI-PIY) and change management (KSI-CMT), with NIST 800-53 control IDs attached as cross-references for Rev 5 assessors. One set of evidence serves both paths. Pinpoint the exact control and container image for any failure. Demonstrate compliance with controls for NIST 800-53 and 800-190 and from the Secure Software Development Framework as codified in NIST 800-218.


Evaluate vulnerabilities by likely exploitability
FedRAMP 20x gives you as few as 2 days to evaluate a finding. Anchore puts CISA KEV status, EPSS, SSVC data and Anchore Score on every finding, so that time goes to decisions, not data gathering. Record affected or not-affected status as VEX annotations, and add findings to an allowlist with time limits and alerts so remediation lands inside required timelines. KEV findings follow CISA’s catalog due dates under BOD 26-04, regardless of PAIN rating. SSVC decisions pair CISA’s exploitation and automatable data with your VEX status, so your team documents likely exploitability and the inputs behind each PAIN rating.
Registry monitoring
Under the VDR rules, a failure in your detection process is itself a vulnerability, so an unscanned registry or a stale feed becomes an assessor finding. Automate continuous scanning of every registry image so coverage matches your authorization boundary, and use Anchore’s admission controller to keep unscanned or noncompliant images out of production.

Persistent validation of production
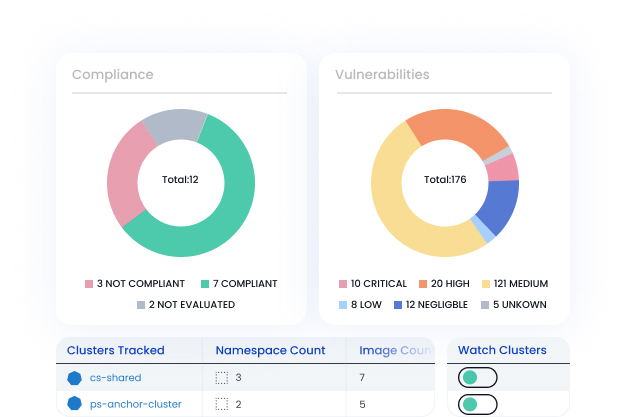
FedRAMP 20x replaces periodic continuous monitoring snapshots with persistent validation: at least every 7 days for Class B and every 3 days for Class C. Anchore continuously inventories container images running in Kubernetes, identifies new vulnerabilities, evaluates policy and alerts on violations. Group findings by application and version, as the VER rules encourage, so one CVE across dozens of images becomes one tracked response instead of dozens of tickets. Scheduled reports cover the monthly human-readable summary.
Streamline FedRAMP 20x reporting
Findings not fully remediated within 192 days of evaluation are reported as accepted vulnerabilities instead of POA&M entries. In Anchore, a time-based allowlist with a rationale, trigger ID and expiry is that accepted-vulnerability record, ready for your GRC tool. Give assessors and agency customers machine-readable evidence instead of screenshots: SBOMs in SPDX and CycloneDX, VEX and VDR documents, and pass/fail policy reports, all through the API.
Download the FedRAMP 20x checklist for containers and SBOMs to share with your security, engineering and compliance teams.

 What are the FedRAMP requirements for vulnerability scanning?